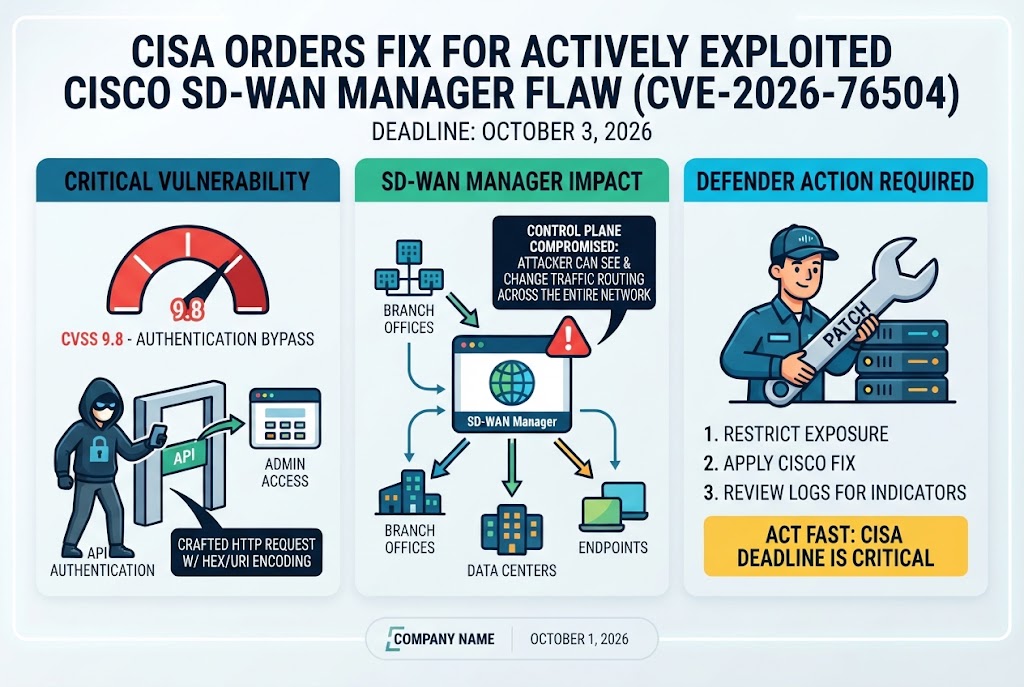
A critical authentication bypass in Cisco Catalyst SD-WAN Manager is being actively exploited, and the U.S. Cybersecurity and Infrastructure Security Agency has ordered federal agencies to deal with it within days. The flaw, tracked as CVE-2026-76504, carries a CVSS score of 9.8, according to a report from The Hacker News.
CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on September 30, 2026. Federal Civilian Executive Branch agencies have until October 3, 2026 to remediate.
How the Flaw Works
The bug lets an unauthenticated remote attacker reach the system with administrator privileges. The weakness stems from improper handling of hex and URI encoding. By sending a crafted HTTP request to the affected system’s API, an attacker can bypass authentication and gain admin access to the API.
SD-WAN Manager is the control plane for Cisco’s software-defined wide area networking. An attacker with admin rights there can see, and potentially change, how traffic is routed across branch offices and data centers. That makes a bypass at this layer far more serious than a flaw in a single endpoint.
Exploitation Confirmed in September
Active exploitation was confirmed in September 2026. The report does not identify the threat actor behind the attacks, the number of victims, or when exploitation began. It also does not list the affected and fixed software versions, so administrators should check Cisco’s advisory directly for patch guidance.
Jake Knott, head of threat intelligence at watchTowr, noted how familiar the pattern has become. “Cisco SD-WAN feels like an ever-present staple of the CISA Known Exploited vulnerabilities list,” he said.
What Defenders Should Look For
The report lists specific indicators for teams hunting for compromise. Administrators can audit the service proxy access log at /var/log/nms/containers/service-proxy/serviceproxy-access.log for requests to “j_security_check” from IP addresses they do not recognize.
They can also search /var/log/nms/vmanage-server.log for “j_security_check” entries with usernames beginning with “viptela-reserved-“. Finally, they should look for POST requests to URL-encoded variants of “/j_security_check”, which suggest an attacker is trying to slip past authentication checks by encoding the path.
Patching Guidance and Open Questions
Several questions remain open. Cisco has not been quoted in the report on the number of affected customers, and the report does not say whether patches are available for every supported release. Until that is clear, organizations that cannot patch immediately should restrict access to the SD-WAN Manager interface to trusted networks and monitor for the log patterns above.
Security teams should also assume that a successful bypass could leave behind persistent access. An attacker with administrator rights on the API can create accounts or change configurations, so a clean log is not proof of a clean system. Credentials and configurations on exposed systems deserve review after patching.
Why the Deadline Matters Beyond Government
CISA’s KEV deadlines bind only federal civilian agencies, but the catalog is widely used as a priority list by private companies. A listing means attackers are already using the flaw, which moves it above vulnerabilities that are merely severe on paper.
Organizations running SD-WAN Manager should treat the three-day federal deadline as a practical benchmark. That means confirming whether their management interfaces are exposed to the internet, applying Cisco’s fix as soon as it is confirmed for their release, and reviewing logs for the indicators above going back to at least September.
A Recurring Problem for Network Management Tools
Knott’s remark points to a broader issue. Network management platforms sit in privileged positions, often reachable from many parts of an organization, and they have become frequent targets. When one fails at authentication, the consequences extend to every device it controls.
For security teams, the lesson is to limit exposure of management planes, monitor them as closely as production systems, and be ready to patch within days, not weeks, when CISA adds a listing.
Leave a Reply